Security & BackupsTutorial
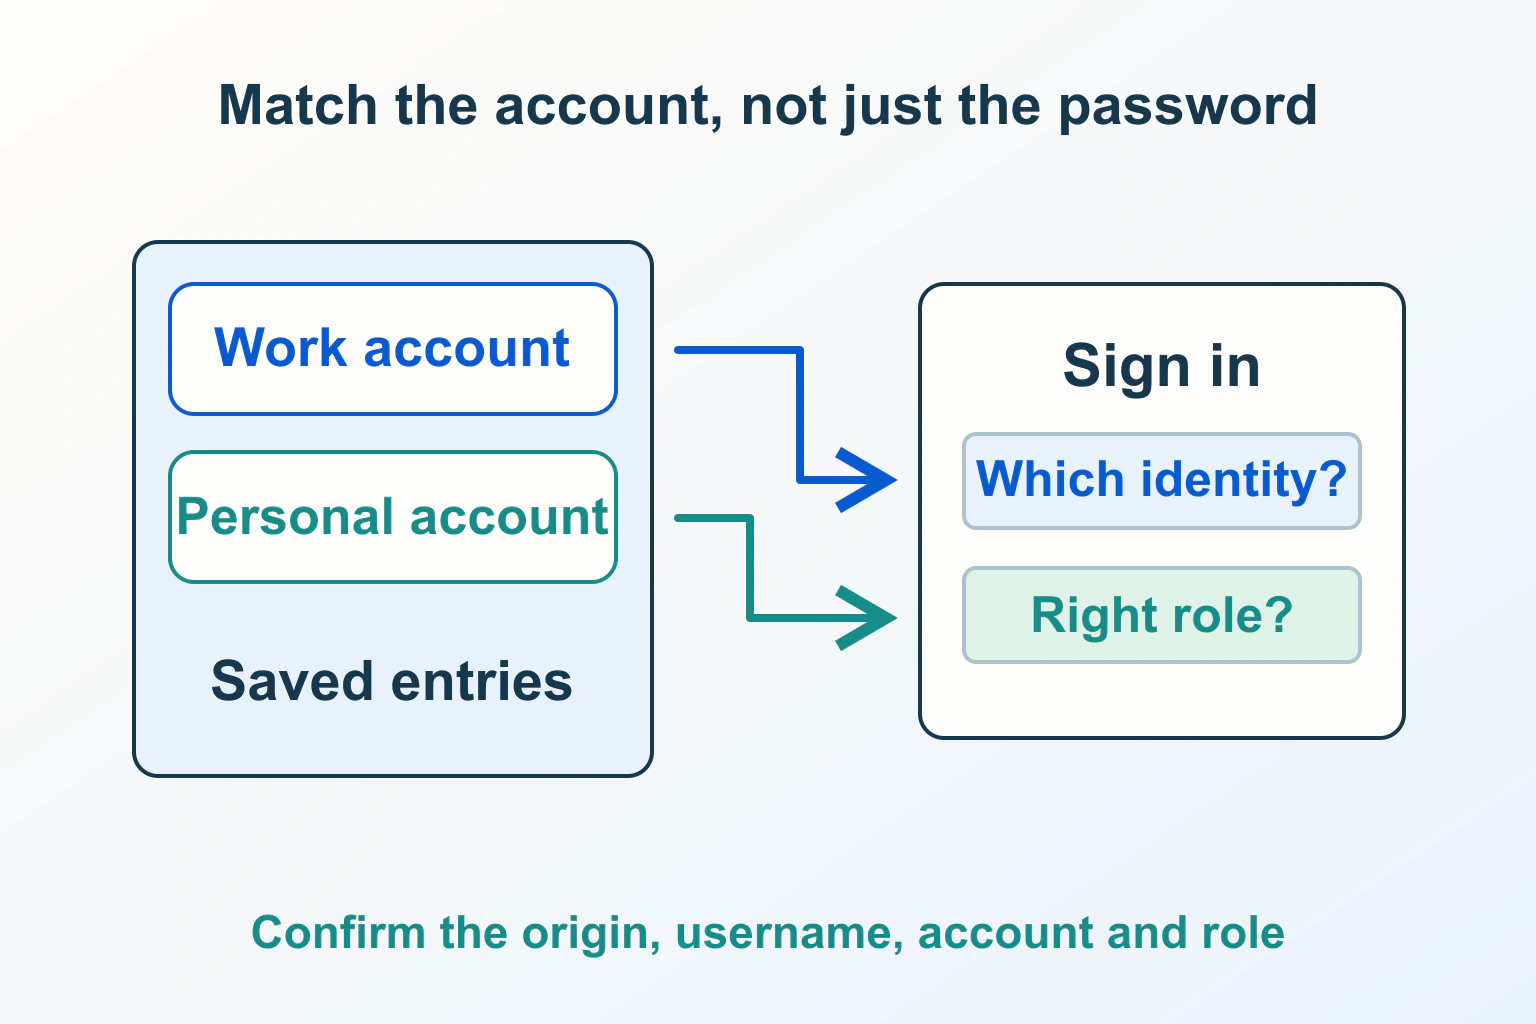
When a password manager selects the wrong login, compare the destination, saved username, account context and competing autofill sources before editing or deleting anything.

Security & BackupsTutorial
Choose the right recovery path after losing a passkey device: another synced copy, an independently enrolled credential, or the website’s documented recovery process.
Security & BackupsTutorial
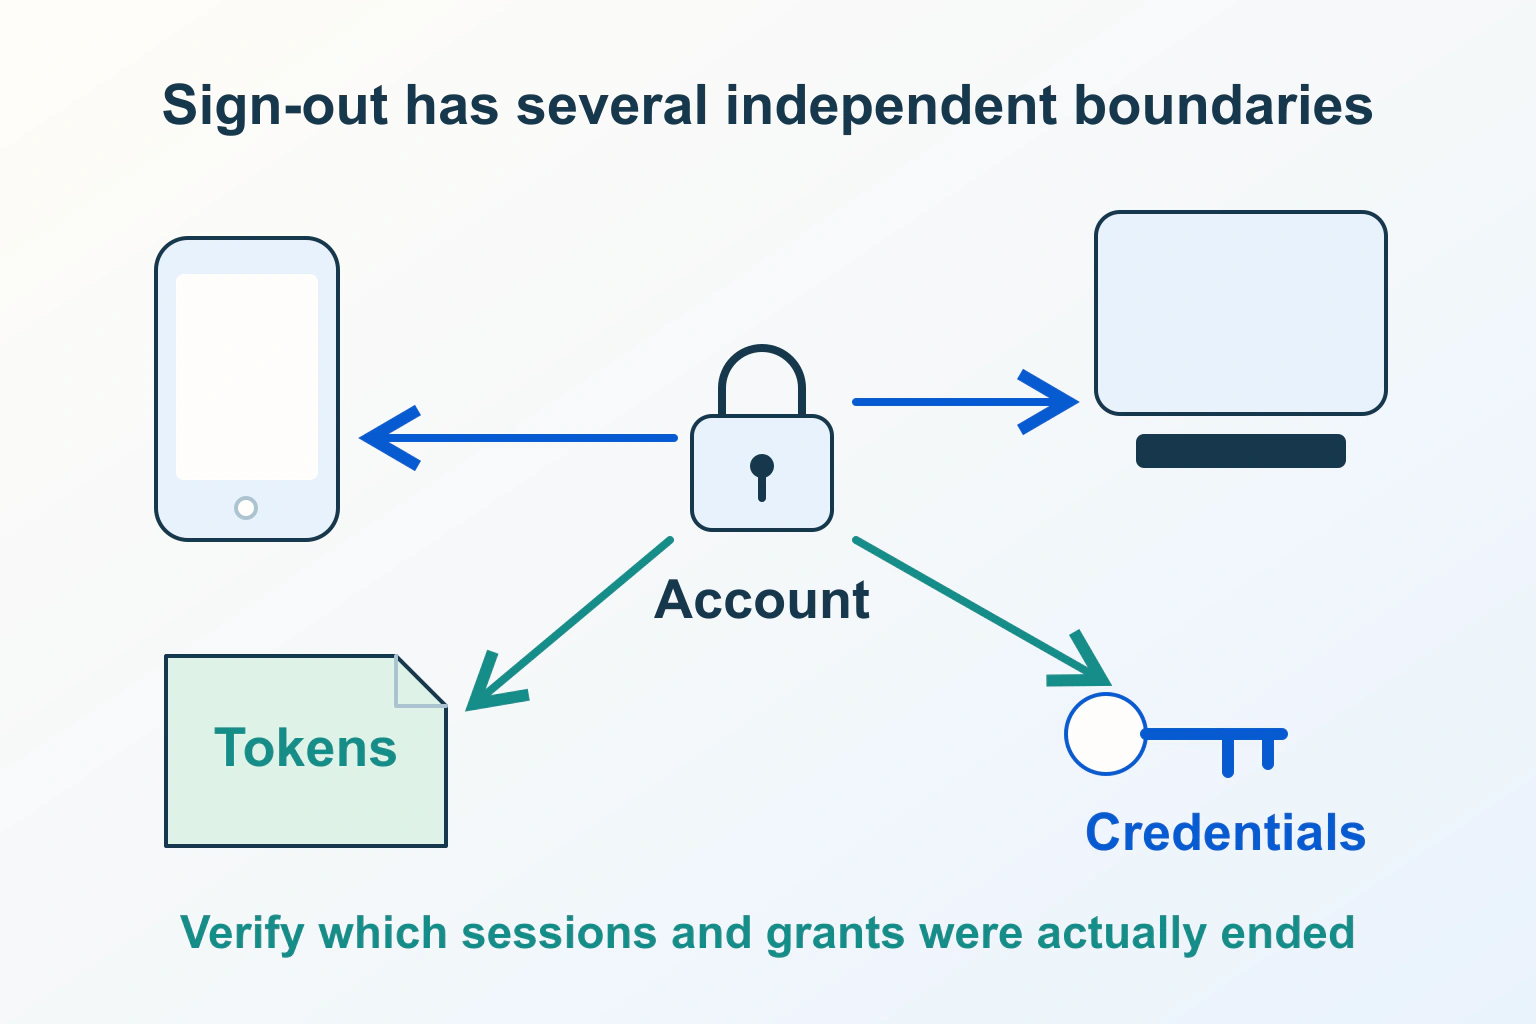
An account-wide logout should end the intended sessions. Check mobile access, background tokens and saved sign-in credentials as separate boundaries.
Security & BackupsTutorial
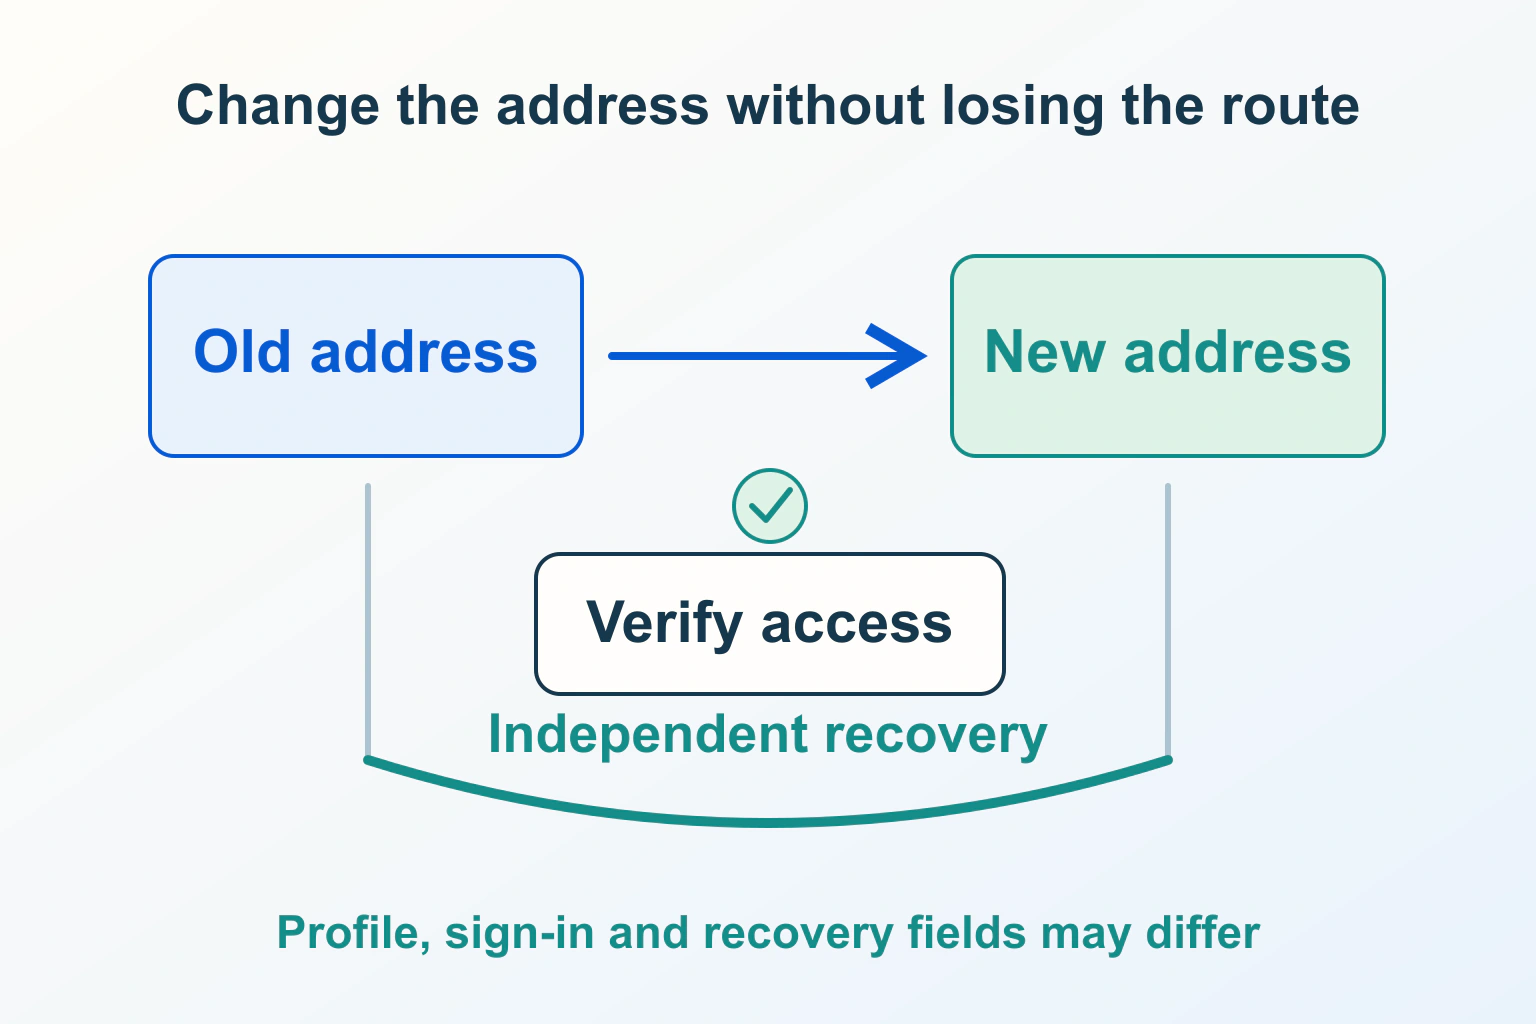
Keep identity, notification and recovery addresses distinct. Confirm the new mailbox, follow the service’s change flow and verify fresh access before retiring the old route.
Security & BackupsTutorial
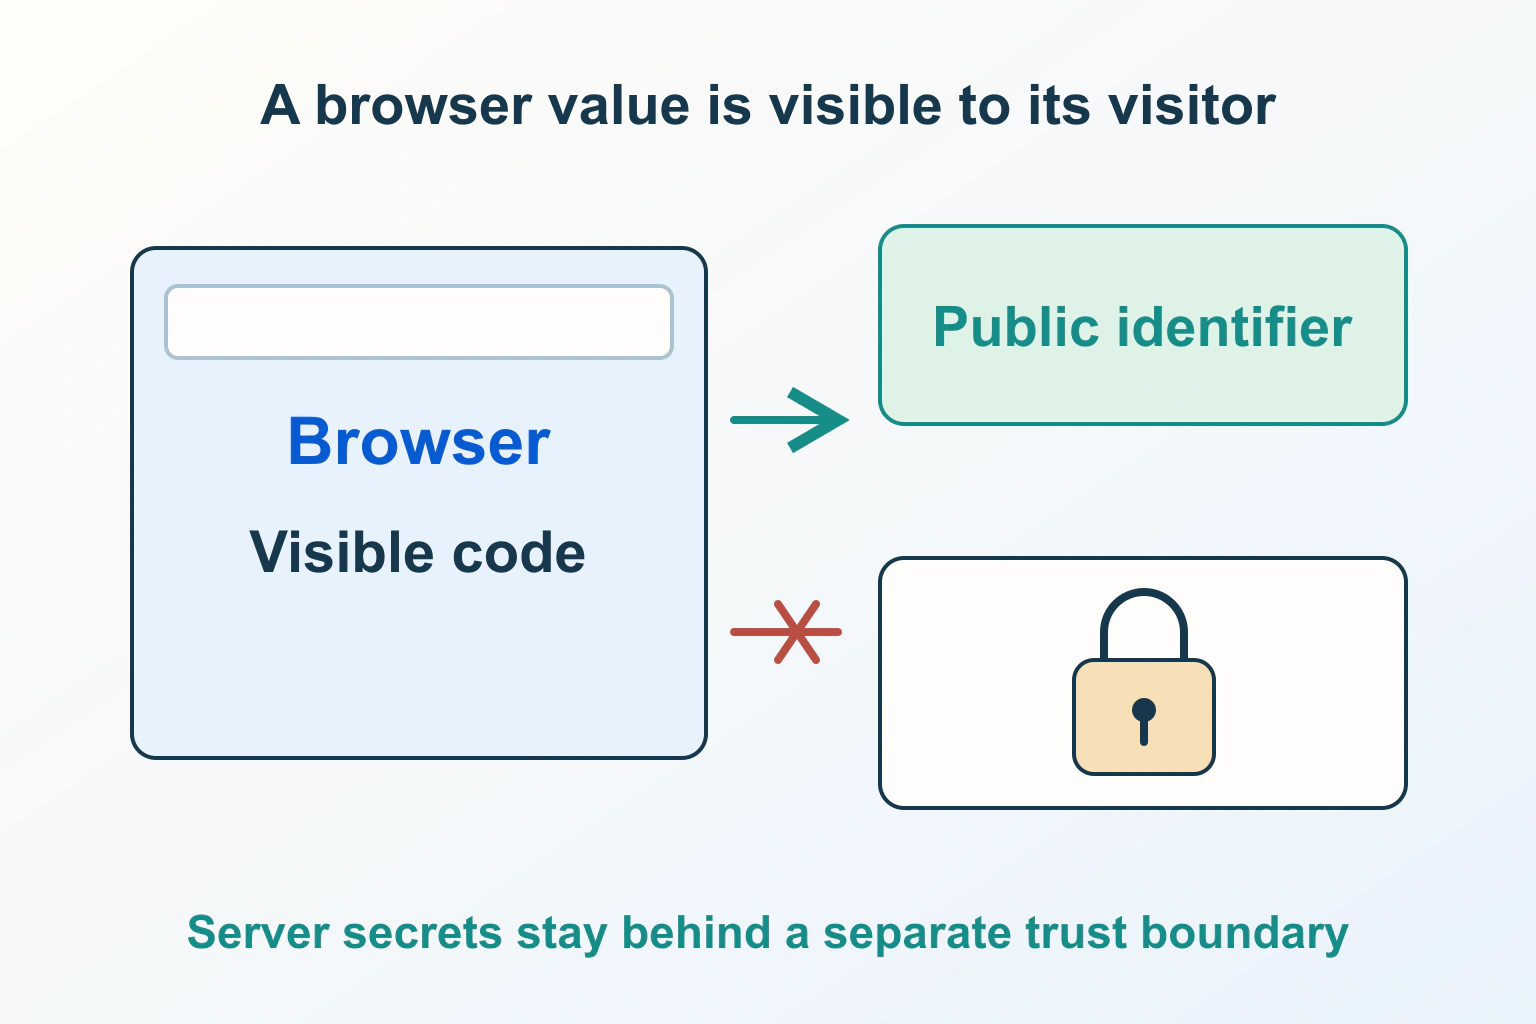
Classify a browser-visible key by its documented authority and restrictions. Public client identifiers differ from privileged credentials; uncertain secrets need containment and rotation.

Security & BackupsTutorial
A backup file, its decryption material and access to the recovery process are separate dependencies. Map them, break circular access and rehearse a safe restore.

Security & BackupsTutorial
Separate the destination address from the referring page. Choose an intentional referrer policy and inspect what leaves public, account and recovery pages.

Security & BackupsTutorial
When login succeeds but does not last, follow the session from cookie issuance to server acceptance. Preserve unsaved work and distinguish intended expiry from a defect.

Security & BackupsTutorial
A refused page or API request needs a precise access diagnosis. Separate authentication challenges, permission decisions and delivery rules without opening private resources.
Security & BackupsTutorial
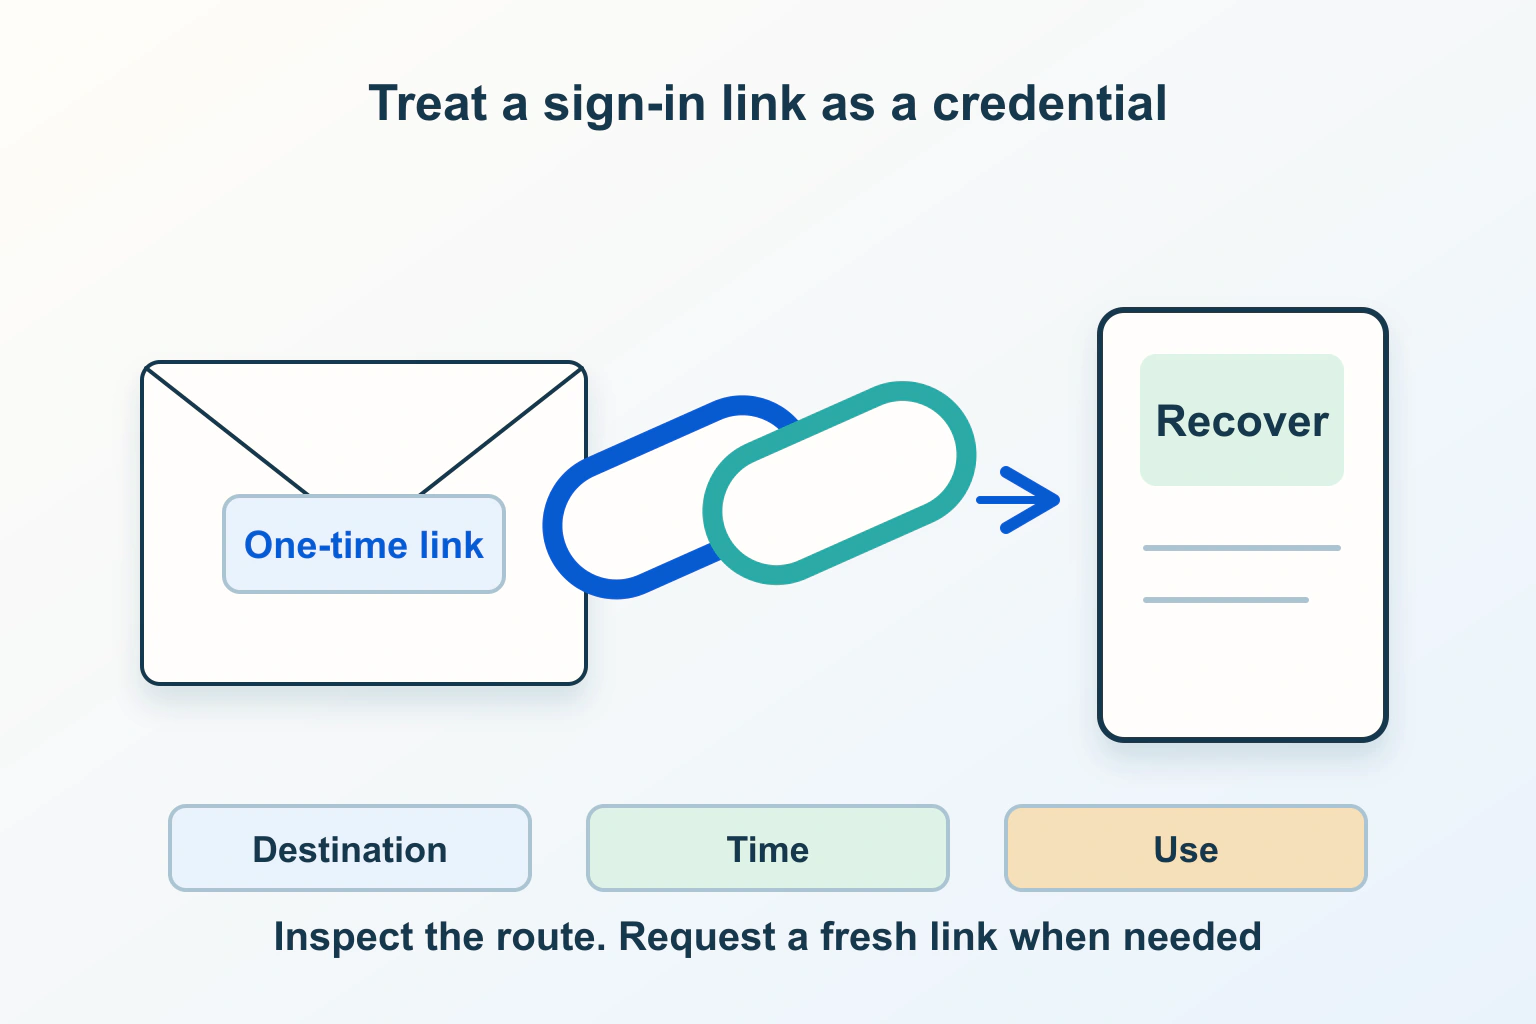
A sent email is only one part of account recovery. Distinguish an absent message, expired or consumed link, wrong destination and a completed action with unclear feedback.
Security & BackupsTutorial
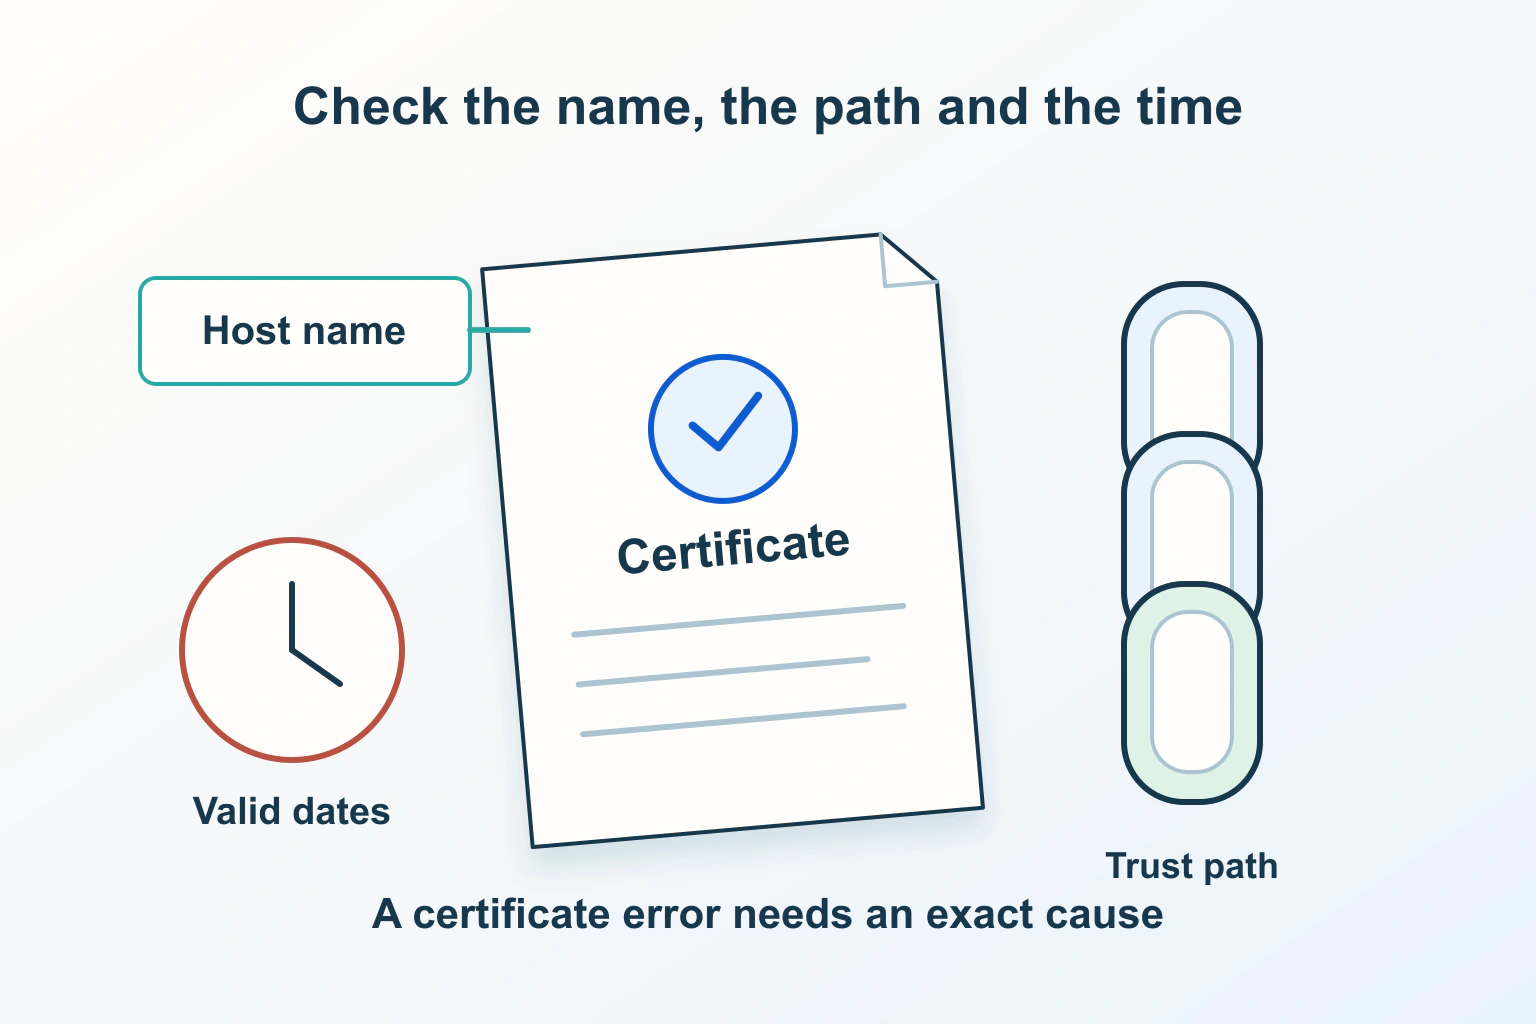
Capture the exact browser warning and public hostname before changing certificates. Separate date, identity and trust failures, and check the certificate visitors actually receive.

Security & BackupsTutorial
Read the final response, identify which policy owns a violation and test a scoped candidate before enforcement. Keep security boundaries and working reader journeys together.
